Complete Control
 Complete Control
Everything you need to build, ship, and scale.
Powerful infrastructure controls designed for modern developers. Manage your deployments, networking, and scaling effortlessly from a clean dashboard or CLI.
Automatic Deploys on Every Git Push
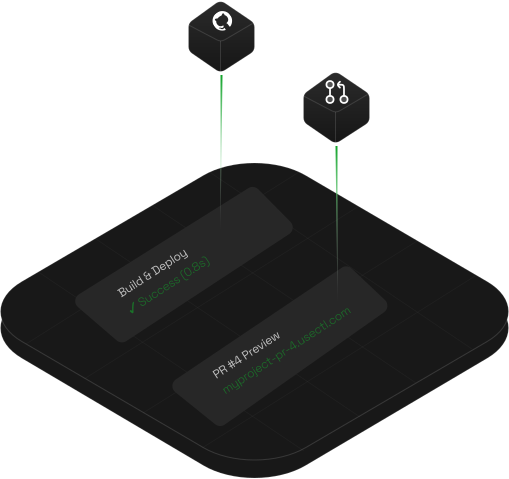
Connect a GitHub repository once and let usectl handle the rest. Every push to your tracked branch builds and deploys automatically, and pull requests can get their own temporary preview environments.

GitHub Integration
Connect a GitHub repository and every push to your branch starts a build.
*.usectl.com

PR Preview Environments
Turn on previews and every pull request gets a temporary URL, removed when the PR closes.
Layer caching

Cached Container Builds
Container builds reuse cached layers, so unchanged steps are skipped on every deploy.
Edge Routing & Custom Domains
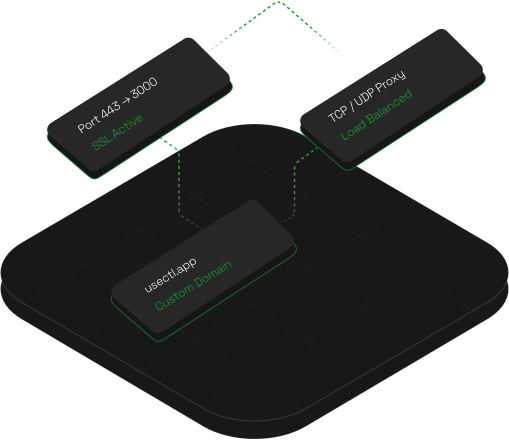
Traffic enters through Cloudflare’s global edge with automatic TLS, then is load-balanced across your replicas. Start on a free usectl.com subdomain or bring your own domain.
Free usectl domain

Public Networking
Expose your application to the public internet instantly with automated routing and TLS.
Isolated

Private Networking
Services in a machine reach each other over internal DNS, while network policies keep other tenants out.
Cluster-internal

Internal TCP & UDP Ports
Open extra TCP or UDP ports so sibling services can reach them. Public traffic is HTTP(S).
Horizontal & Vertical Scaling
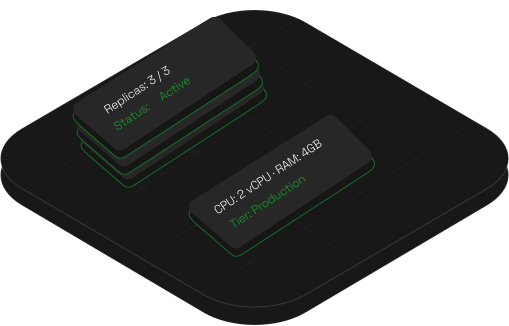
Scale your application on your terms. Set the replica count of any app, or resize its CPU and memory to handle heavier workloads.
Replica count

Horizontal Pod Replicas
Set your instance count with one CLI command (usectl machines pods set <machine> <pod> replicas=N).
vCPU & RAM tuning

Granular Resource Sizing
Tune CPU and memory for each app, down to 100m CPU and 128 MiB, to match your workload.
Zero-downtime rollouts

Rolling Updates
New pods come up before old ones stop, so a deploy doesn’t take your app offline.
Real-Time Telemetry & AI Incident Response
Comprehensive observability powered by Mimir, Loki, and Tempo. Monitor resource health, track traffic metrics, and let the AI incident agent diagnose alerts and propose fixes you approve.
No Prometheus server

Metrics & Tracing Stack
High-performance telemetry powered by Grafana Alloy, Mimir, Loki, and Tempo for complete visibility.
Optional auto-rollback

Deploy-Safety Watcher
Turn it on and usectl rolls a deploy back if the HTTP 5xx rate stays above a safety threshold after release.
Qwen3-14B AI

AI Incident Agent
When an alert fires, an LLM reads logs, metrics and recent deploys, explains the likely cause and proposes a fix you approve in one tap.
Defense-in-Depth Security & Sandboxed Isolation
Layered security featuring network-isolated agent sandboxes, strict per-namespace network policies, a built-in encrypted secret vault, and AI guardrails.
Internet-only egress

Isolated Agent Sandboxes
Hosted AI agents run in their own pods behind a network policy: they reach the public internet and nothing else in the cluster.
AES-256-GCM

Vault Envelope Encryption
Store sensitive secrets safely with AES-256-GCM encryption, hash-chained audit logs, and write-only protected variables.
Zero Direct Write

AI Copilot Guardrails
Maintain strict human oversight with “Model Proposes, Human Approves” workflows and scoped agent API keys.
Scoped Variables & Secure Configurations
Manage environment variables and secrets at machine or pod level, with write-only protection and encryption at rest.
Pod-level scoping

Pod-Scoped Variables
Bind environment configurations specifically to target pods rather than the entire machine for precise control.
Write-only

Write-Only Secrets
Protected variables are never shown again after saving, and sensitive keys are masked in the dashboard and CLI.
AES-256-GCM

Encrypted Variables
Environment variables are stored with AES-256-GCM encryption, and every change is logged: who and when, never the value.
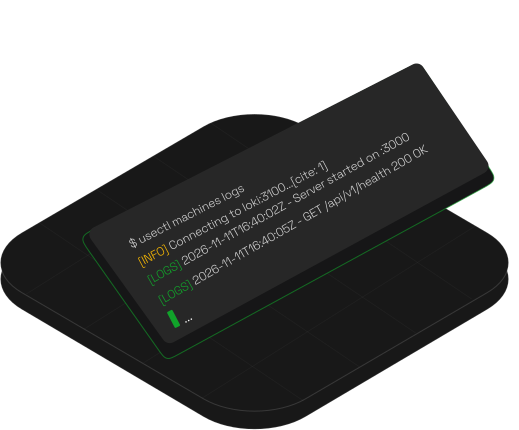
Real-Time Logs & Interactive Terminal
Diagnose issues quickly: search logs stored in Loki, live-tail any pod from the CLI, or jump into a secure interactive terminal inside a container.
Loki-powered

Centralized Log Search
Search and filter container logs across your machine, stored in Loki, from the dashboard or your AI tools over MCP.
Secure exec

Interactive Terminal Access
Execute diagnostic commands safely inside target containers directly from your CLI or web dashboard.
Node-level agents

Alloy Log Collection
Benefit from efficient, node-level log harvesting managed seamlessly by Grafana Alloy agents.
Secure sandboxes & autonomous OPS
Put your agents to work on usectl
Host open-source AI agents in network-isolated sandboxes and let built-in copilots manage your infrastructure.